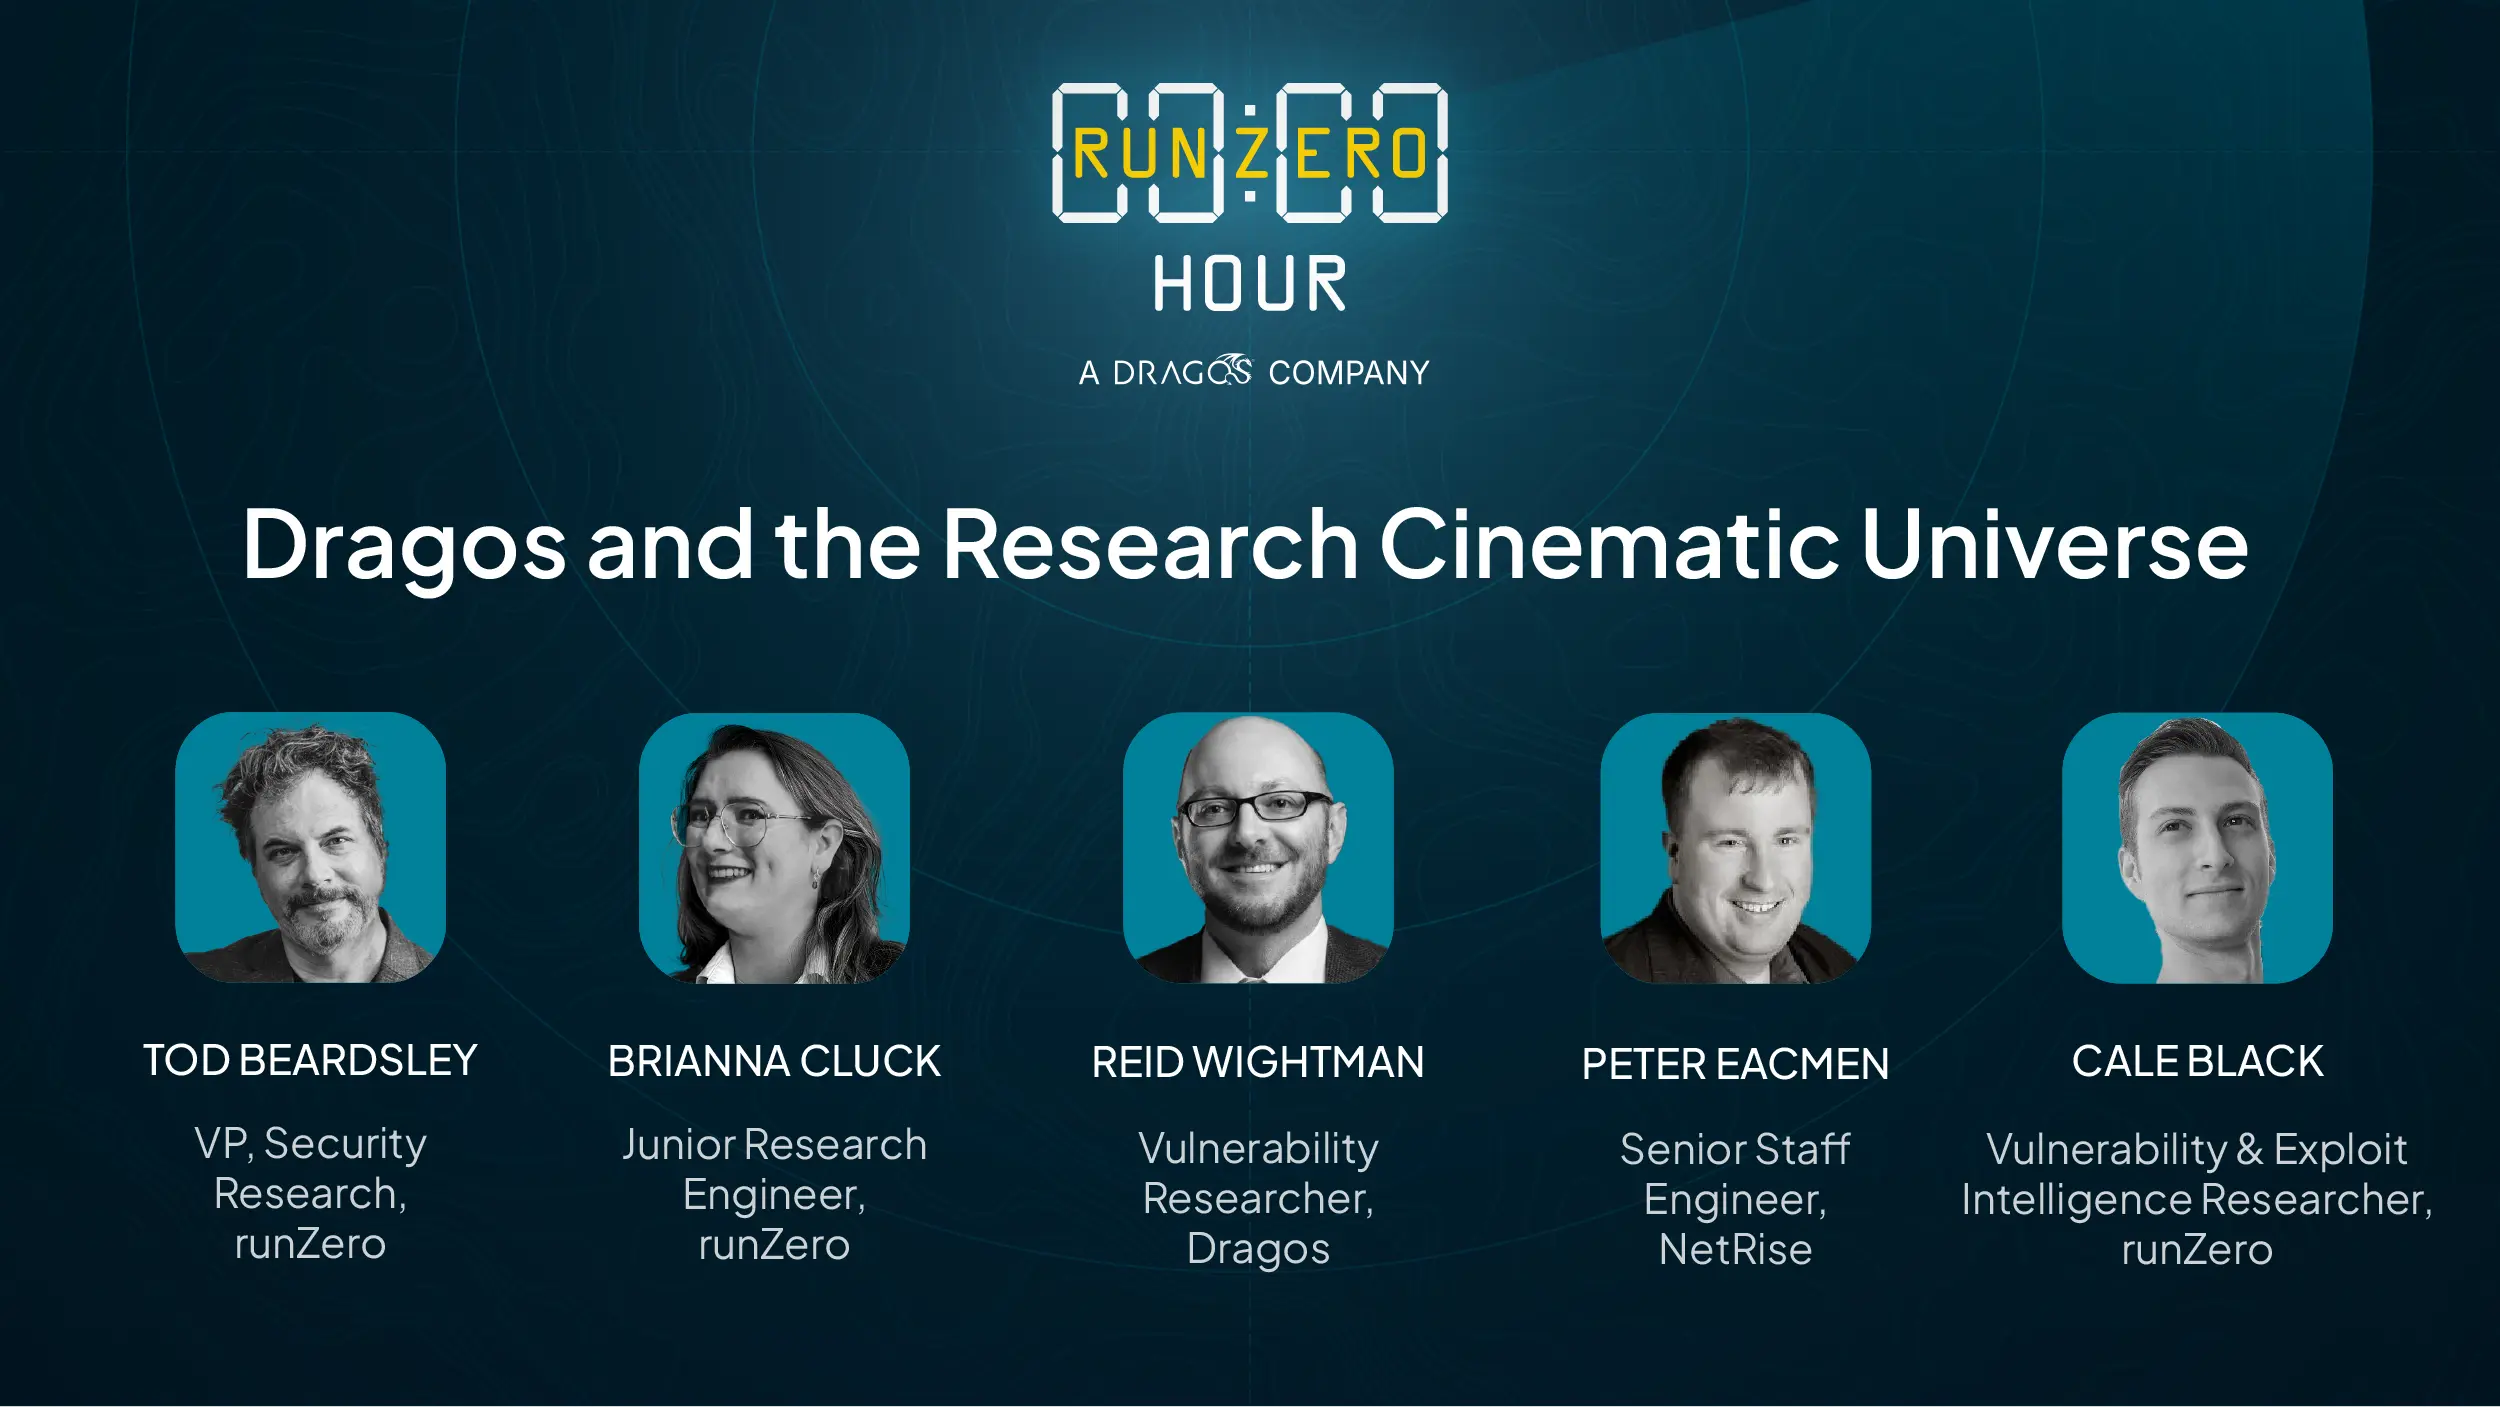
As you no doubt have heard, Dragos, NetRise, and runZero have all joined forces, in one epic Dragos extravaganza (or, exDragoganza?) and we here in cybersecurity research cannot be more pleased about what lies ahead, for reasons we think are obvious. The community and our customers might be wondering why this is so significant, though. This is why we planned to talk about all this on the latest episode of runZero Hour, Dragos and the Research Cinematic Universe, from specifically a research perspective, but alas, we were overtaken by events and ended up explaining and opining on the fresh new php2shell vulnerabilities that were published that very morning.
And opine we did, from some very different perspectives! This is exactly the kind of thing I expected when I first learned of this merger. One fresh new infosec crisis, several new angles and vectors to consider.
At runZero, querying for newly-discovered vulnerable software is our day-to-day; we keep tabs on vulnerability intelligence, we pick out what we think is about to become a real problem for our customers and users, and we enable IT shops around the world to find those assets that exhibit the issue.
Our new company-mates at NetRise have a different approach. A lot of times, you don’t know exactly what’s in the devices that blink and buzz on your network, and it’s entirely possible the company that made that thing also doesn’t know. So, you need to tear down the firmware to verify things like specific versions and builds of components.
Dragos, on the third hand, is very much in the OT and xOT space, and they know that you can’t just go running around an OT environment all willy-nilly, firing off network probes on services that run on funny ports; that way leads to crashed factory floors and interrupted power distribution.
So, if you take the broad exposure management smarts of runZero, the firmware spelunking know-how of NetRise, and the deep bench of OT experience from Dragos, and mix them all together, you almost can’t help but have some truly awe-inspiring outputs. I’m looking forward to synthesizing all this research talent across our combined products, so at the end of the day, we can offer powerful, versatile, and most of all, safe active and passive asset management no matter what the form factor or level of visibility you might have today.
runZero knows tons of networking tricks to tease information out “the hard way,” as HD put it during the founders webcast just a couple days ago. Dragos knows where all the rakes are laid out in OT environments. NetRise knows how to extract the truth about firmware composition. Of course, we all have built up our libraries over years of real-world experience. Combining all this will take some work, sure, and challenging some fundamental technical assumptions along the way, as well as getting challenged on the same, but I’m here for it.
I’ve found that the news about the merger often uses Voltron metaphors about robot body parts, but as this blog title suggests, I’m more of a Captain Planet guy. After all, cybersecurity is all about saving the world and responding to crises, fairly routinely, and I’m taking Dragos’ “safeguarding civilization" mission to heart. Because saving our planet is the thing to do.