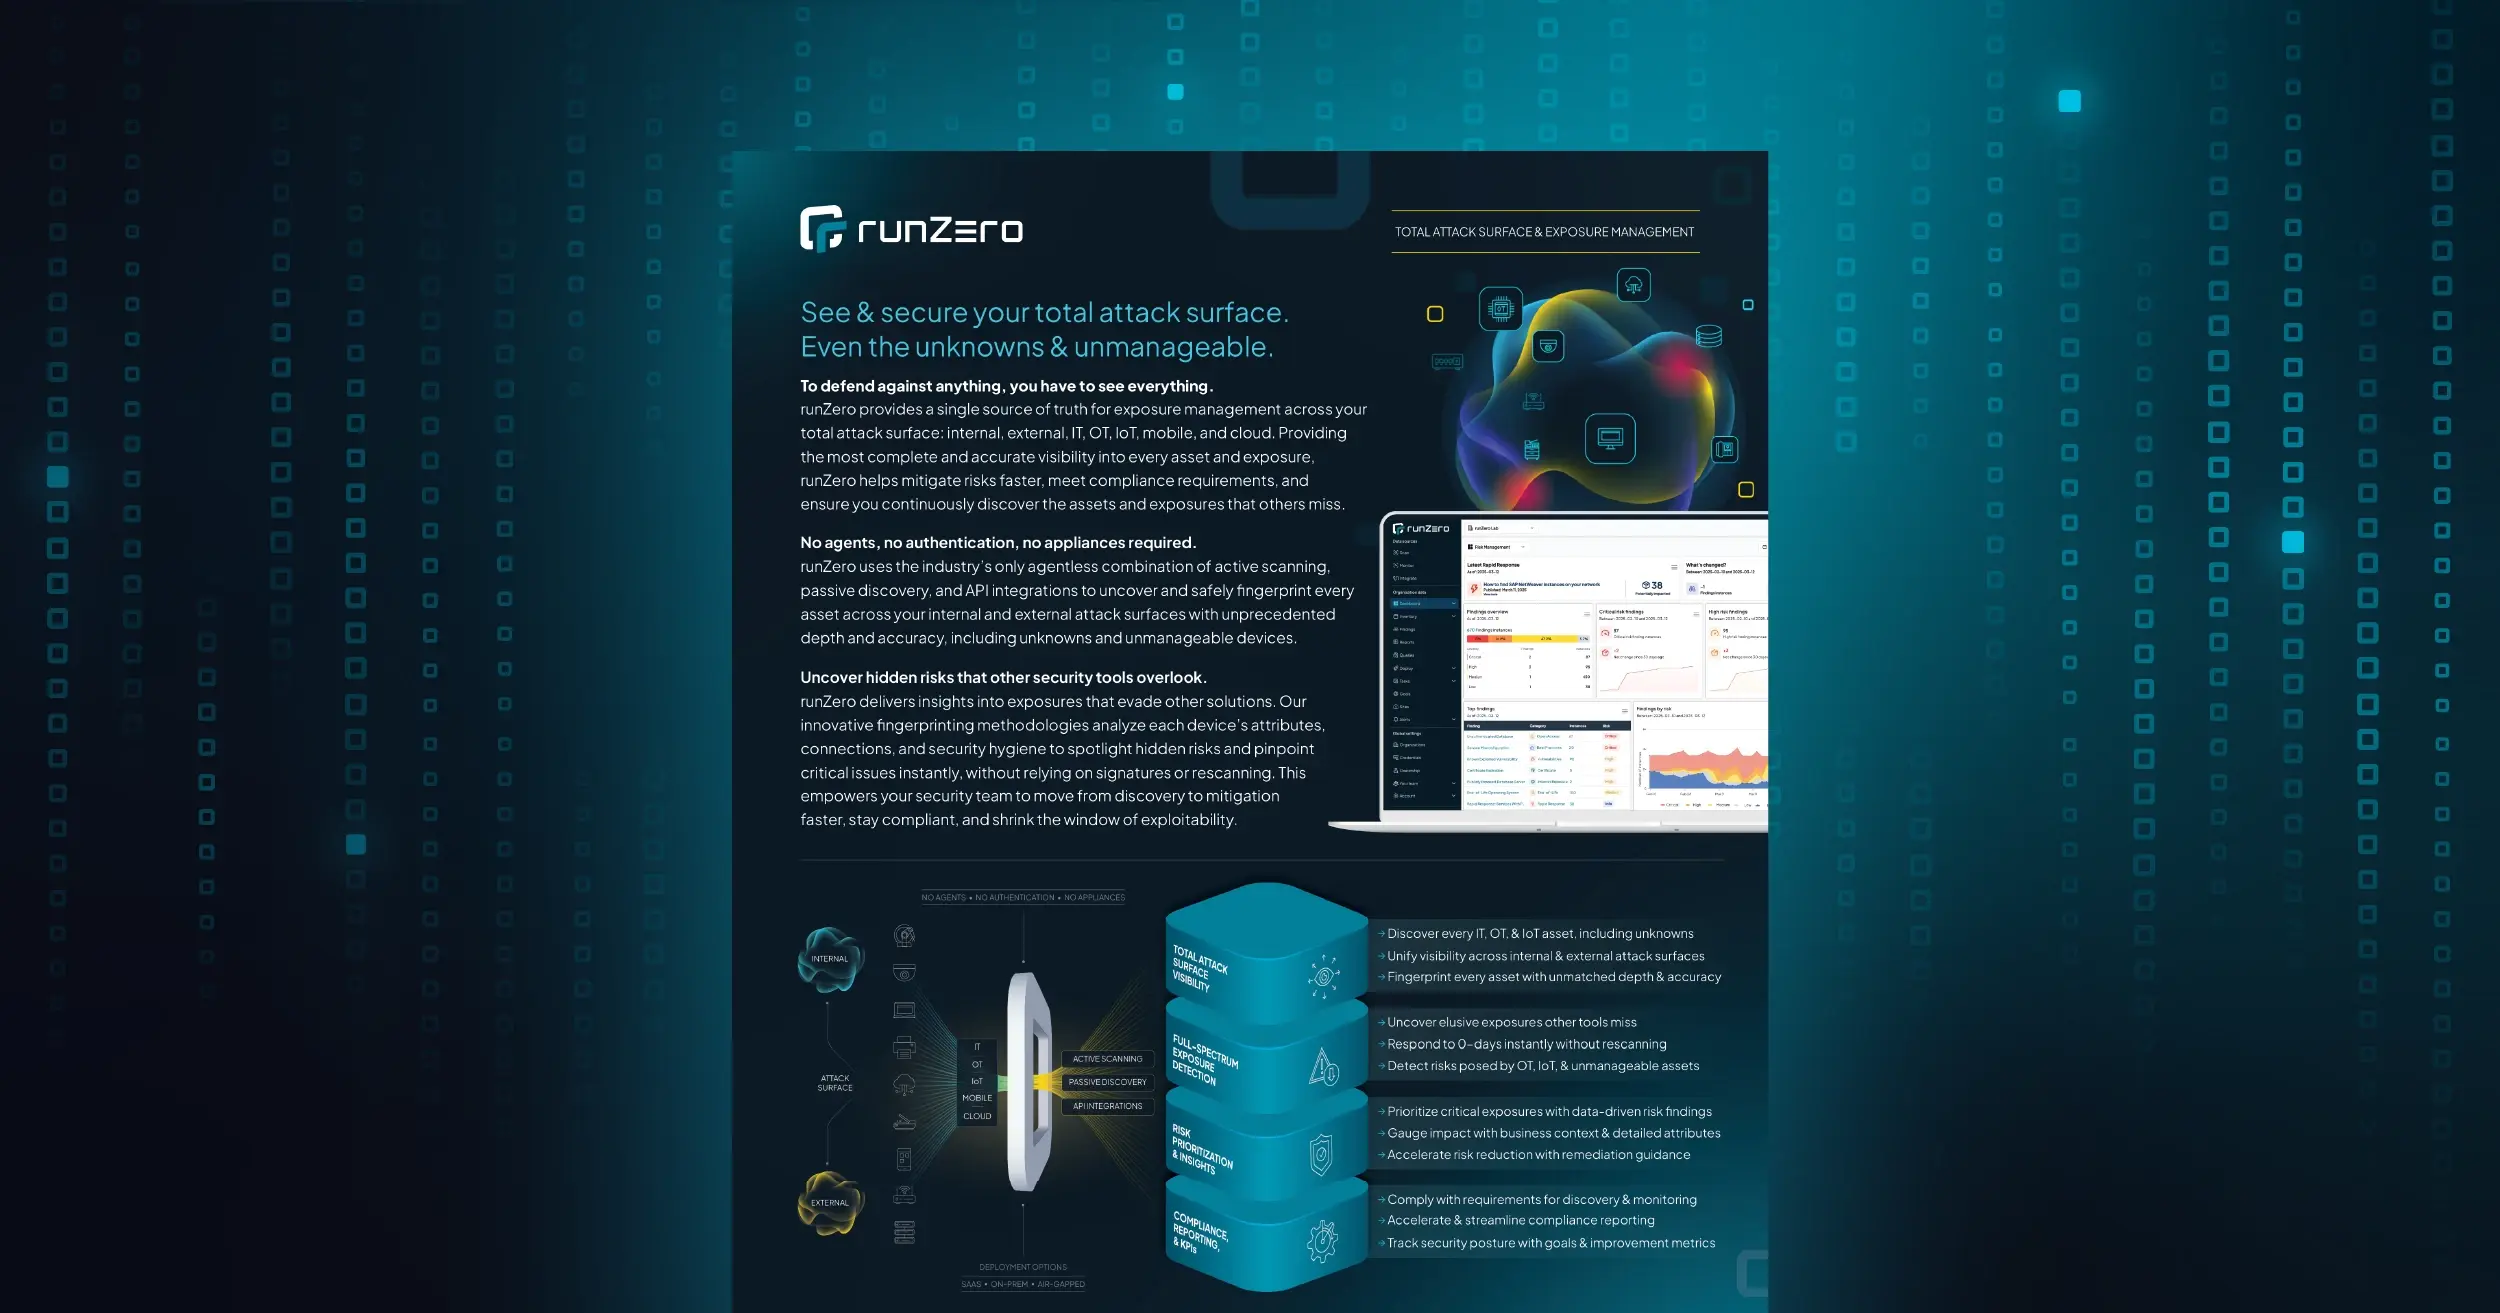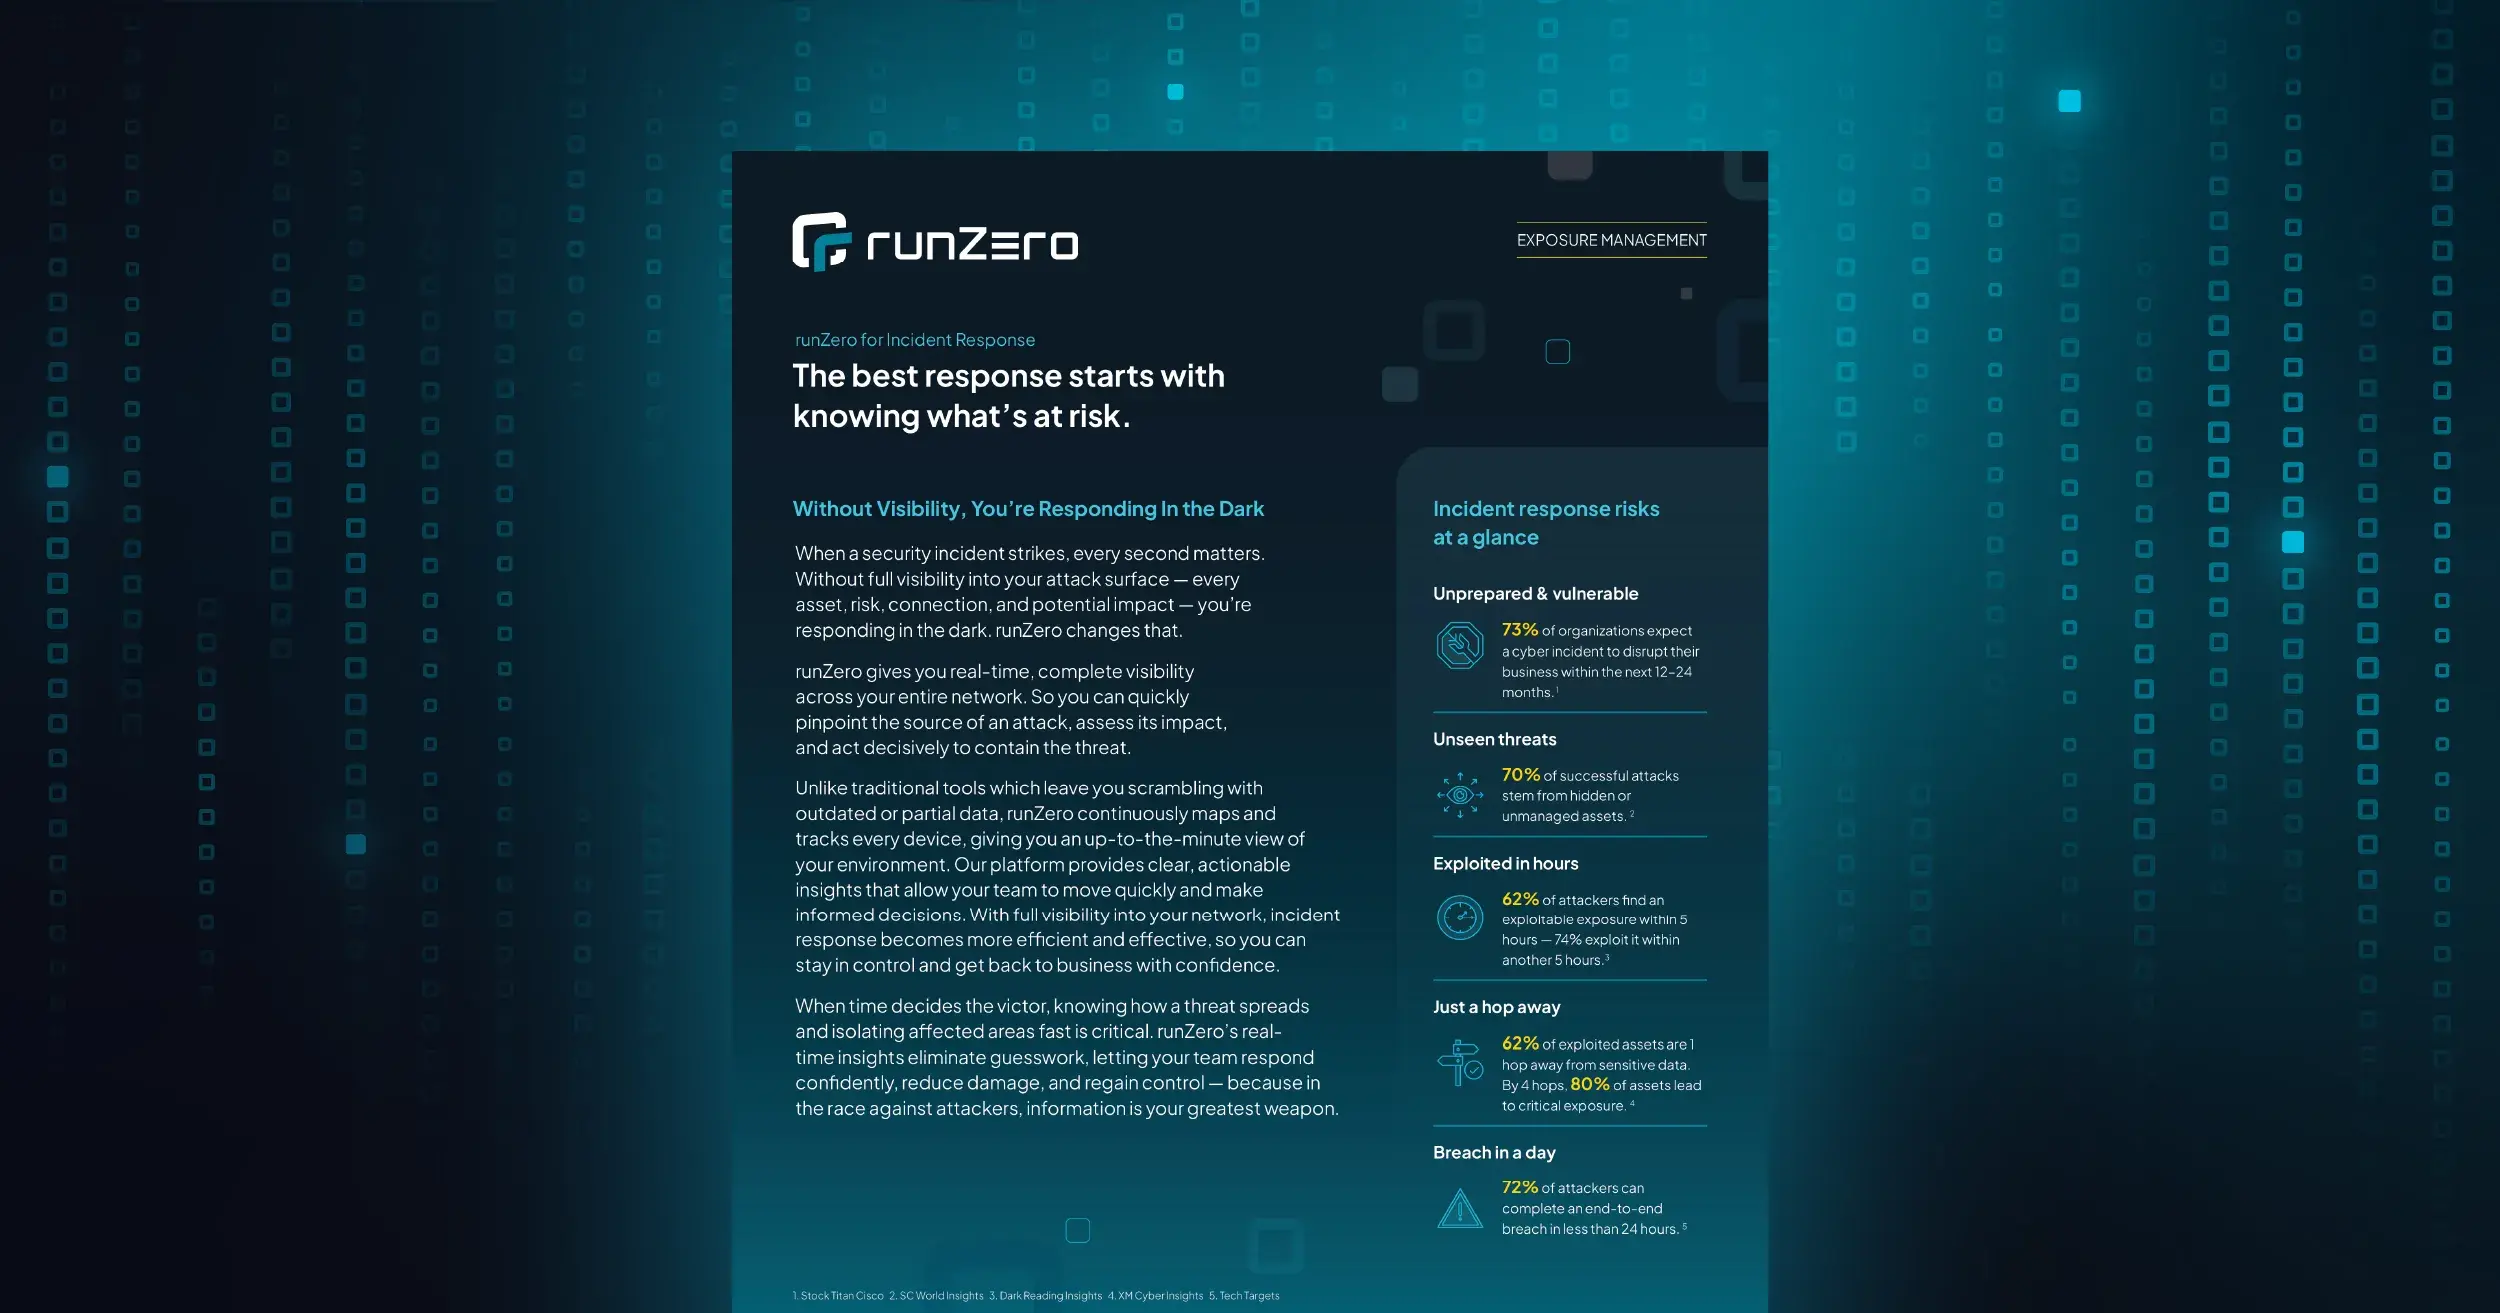
Federal agencies have heavily invested in cybersecurity and accelerated Zero Trust adoption, yet breaches persist through the very systems they rely on most. Traditional discovery tools leave up to 25% of network assets completely invisible — precisely the unmanaged devices targeted in nearly three-quarters of successful attacks.
Beyond total blind spots, critical perimeter appliances are frequently compromised or lack the logging capabilities required to detect initial entry points.
Download the full report to explore how to eliminate critical asset visibility gaps and safeguard legacy, OT, and vendor-managed environments without disrupting operations.