




OpenSSH password authentication bypass: CVE-2026-123158 #
OpenBSD disclosed that certain versions of OpenSSH are affected by a password authentication bypass. Specifically, the sshd server in versions prior to 10.6p2 lacks a workaround when running on Linux systems that use musl libc without PAM. The bug stems from a misinterpretation of whether a string is intended to be a password hash. On some account configurations, any password between 256 and 1024 characters succeeds, allowing a remote, unauthenticated attacker to log in as an account that has no password set (for example, a key-only account whose password field is "*"). Exploitation requires at least one other local account with a "$5$" or "$6$" password hash and PasswordAuthentication enabled, which is the default. Alpine Linux is an example of a platform that uses musl libc without PAM in its default openssh-server package. This vulnerability has been designated CVE-2026-123158 and has been rated high with a CVSS score of 8.1.
The following versions are affected
- OpenSSH: Versions prior to 10.6p2 on Linux systems using musl libc with PAM disabled
- Alpine Linux openssh: Versions prior to the fixed package for each release branch listed below, and openssh-server-pam with "UsePAM no"
What is OpenBSD OpenSSH? #
OpenSSH is a widely used implementation of the SSH protocol that provides secure remote login, command execution, and file transfer.
What is the impact? #
Successful exploitation of this vulnerability would allow a remote, unauthenticated attacker to bypass password authentication and gain unauthorized interactive access to target Linux systems under eligible account configurations, potentially leading to unauthorized data exposure and full host compromise.
Are any updates or workarounds available? #
Users are encouraged to update to the latest version as quickly as possible:
- OpenSSH: Upgrade to version 10.6p2 or later.
- Alpine Linux openssh edge: Upgrade to 10.6_p2-r0 or later.
- Alpine Linux openssh 3.24: Upgrade to 10.3_p1-r2 or later.
- Alpine Linux openssh 3.23: Upgrade to 10.2_p1-r1 or later.
- Alpine Linux openssh 3.22: Upgrade to 10.0_p1-r11 or later.
- Alpine Linux openssh 3.21: Upgrade to 9.9_p2-r1 or later.
- Alpine Linux openssh 3.20: Upgrade to 9.7_p1-r6 or later.
- Alpine Linux openssh 3.19: Upgrade to 9.6_p1-r3 or later.
- Alpine Linux openssh 3.18: Upgrade to 9.3_p2-r4 or later.
- Alpine Linux openssh 3.17: Upgrade to 9.1_p1-r7 or later.
- Alpine Linux openssh 3.16: Upgrade to 9.0_p1-r6 or later.
Mitigation:
- Set "PasswordAuthentication no" in the sshd configuration and restart sshd.
- On systems that build OpenSSH with PAM support, run sshd with "UsePAM yes".
Finding exposed OpenBSD OpenSSH installations with runZero #
From the Services Inventory, use the following query to locate potentially impacted assets:
(os:Alpine OR os:OpenWrt OR os:Yocto) AND _asset.protocol:ssh AND protocol:ssh AND
ssh.authMethods:password AND _service.product:"OpenBSD:OpenSSH"Note: This query identifies Alpine Linux, OpenWrt, and Yocto systems with an OpenSSH service that offers password authentication. It does not confirm whether the installed package contains the fix.
February 2025: (CVE-2025-26465, CVE-2025-26466) #
The Qualys Threat Research Unit (TRU) disclosed two vulnerabilities discovered in the OpenSSH software:
- CVE-2025-26465 affects OpenSSH clients and allows for a remote attacker to perform a machine-in-the-middle attack, bypassing the client verification of the server's identity. This is possible if the VerifyHostKeyDNS option is enabled, which is disabled by default. Additionally, the currently known exploit methods require exhausting the client's memory first which increases attack complexity. It has been assigned a CVSS score of 6.8.
- CVE-2025-26466 can result in a pre-authentication denial-of-service in both the client and server by exhausting memory and CPU resources.
Are any updates or workarounds available? #
Both vulnerabilities were patched in OpenSSH version 9.9p2, which was released today (February 18, 2025).
How to find potentially vulnerable systems with runZero #
From the Service Inventory you can use the following query to locate potentially vulnerable systems:
_asset.protocols:ssh protocol:ssh (_service.product:="OpenBSD:OpenSSH:9.5%" OR _service.product:="OpenBSD:OpenSSH:9.6%" OR _service.product:="OpenBSD:OpenSSH:9.7%" OR _service.product:="OpenBSD:OpenSSH:9.8%" OR _service.product:="OpenBSD:OpenSSH:9.9p1")August 7th 2024: OpenSSH vulnerability on FreeBSD #
On August 7th, 2024 the FreeBSD security team issued an advisory detailing a vulnerability in OpenSSH when running on the FreeBSD operating system. This vulnerability, designated CVE-2024-7589 has a CVSS score of 7.4 and is rated high.
This vulnerability is similar to the earlier regreSSHion vulnerability disclosed in July of 2024, where a remote attacker is able to trigger an asynchronous signal handler in an unsafe manner. In this case, it is due to the integration of the blacklistd service with OpenSSH on FreeBSD.
What is the impact? #
Successful exploitation of this vulnerability would allow an attacker to execute arbitrary code with root privileges on a vulnerable FreeBSD system.
Are updates or workarounds available? #
The FreeBSD Project has released an update to address this issue and urges all users to update as quickly as possible. Additionally, setting the LoginGraceTime parameter in sshd_config to 0 will mitigate this issue, though it potentially exposes the SSH service to a denial-of-service attack.
How to find potentially vulnerable OpenSSH on FreeBSD systems with runZero #
OpenSSH on FreeBSD is shipped as an integral part of the operating system. The following query can used in the Services Inventory to locate potentially vulnerable systems:
protocol:ssh AND product:OpenSSH AND os:FreeBSD
July 8th 2024: OpenSSH on Red Hat Enterprise Linux (CVE-2024-6409) #
On July 8th, 2024, a vulnerability in OpenSSH running on Red Hat Enterprise Linux and Fedora systems was disclosed. This vulnerability is similar to the earlier regreSSHion vulnerability disclosed on July 1st, 2024, where a remote attacker is able to trigger an asynchronous signal handler in an unsafe manner. In this case, the vulnerability is due to the vendor-specific patches from Red Hat and the Fedora Project. Other Linux distributions derived from these distributions are likely also vulnerable.
This vulnerability has been designated CVE-2024-6409 and has a CVSS score of 7.0.
What is the impact? #
Successful exploitation of this vulnerability would allow an attacker to execute arbitrary code on a vulnerable Linux system.
Are updates or workarounds available? #
Red Hat has released an update to address this issue and urges all users to update as quickly as possible.
How to find potentially vulnerable OpenSSH installations systems with runZero #
The following query can used in the Services Inventory to locate potentially vulnerable systems:
protocol:ssh (_service.product:="OpenBSD:OpenSSH:9%" OR _service.product:="OpenBSD:OpenSSH:8%") os:LinuxJuly 1st 2024: regreSSHion (CVE-2024-6387) #
On July 1, 2024 the OpenSSH team released version 9.8p1 to address 2 vulnerabilities. The most critical of the two allows Remote Code Execution (RCE) by unauthenticated attackers under certain situations. This vulnerability was discovered by Qualys and dubbed "regreSSHion".
CVE-2024-6387 is a critical rated vulnerability in the portable (non-OpenBSD) versions of OpenSSH from 8.5p1 to 9.7p1. Successful exploitation enables attackers to run arbitrary code with root privileges. Note that the "p" in those version strings indicates "portable". Exploitation is currently thought to take multiple hours and use many connections but it is likely that the exploit effectiveness may improve now that the information is public.
A second vulnerability related to the the failure of the ObscureKeystrokeTiming security feature has also been fixed. It was discovered that OpenSSH clients using versions 9.5 through 9.7 did not correctly implement this feature and so may have been susceptible to keystroke timing attacks when connected to an OpenSSH 9.5 or higher server.
What is the impact? #
There are a few things to understand when determining impact and risk of CVE-2024-6387. OpenSSH on OpenBSD is not vulnerable. Also, these exploits currently take multiple hours to work against 32-bit Linux/glibc systems with the Address space layout randomization (ASLR). Exploitation of 64-bit systems is thought to be possible but hasn't yet been demonstrated. Exploitation of non-glibc systems, such as Alpine Linux and various BSD based operating systems, is similarly unexplored.
It is important to keep in mind that this vulnerability will likely draw the attention of very skilled individuals and groups. The definition of "possible" and "likely" may change greatly over the coming days and weeks.
Are updates or workarounds available? #
The OpenSSH team has released version 9.8p1 to address these vulnerabilities. Updates will likely be released for various operating systems very quickly if they haven't been already.
The following vendors have already issued advisories and packages:
- Debian: DSA 5724-1 - OpenSSH security update / Security Tracker
- FreeBSD: FreeBSD-SA-24:04.openssh
- Oracle: ELSA-2024-12468
- Red Hat: CVE-2024-6387
- Ubuntu: USN-6859-1 - OpenSSH vulnerability
How to find potentially vulnerable OpenSSH systems with runZero #
It is important to note that most Linux distributions with scheduled releases and stability guarantees, such as Debian, Red Hat Enterprise Linux, and Ubuntu, will backport the fix to existing versions of OpenSSH instead of updating to 9.8p1. This means that their specific package version numbers may update but the version of OpenSSH may not.
Here is an example for Ubuntu 24.04:
Unpatched:
OpenSSH_9.6p1 Ubuntu-3ubuntu13
Patched:
OpenSSH_9.6p1 Ubuntu-3ubuntu13.3
As a result, auditing any environment will be more complex than normal.
For auditing overall OpenSSH versions go to the Software Inventory and use the following query:
name:"OpenBSD OpenSSH" (version:>8.4 AND version:<9.8)
Specific services can be found using the Service Inventory and the following query which will remove some of the versions known to be patched:
protocol:ssh ( _service.product:="OpenBSD:OpenSSH:9%" OR _service.product:="OpenBSD:OpenSSH:8%" ) NOT (os:OpenBSD OR banner:"OpenSSH_8.0" OR banner:"OpenSSH_8.1" OR banner:"OpenSSH_8.2" OR banner:"OpenSSH_8.3" OR banner:"OpenSSH_8.4" OR banner:"OpenSSH_9.8" OR banner:"OpenSSH_for_Windows" OR banner:"Ubuntu-3ubuntu13.3" OR banner:"Ubuntu-3ubuntu0.10" OR banner:"Ubuntu-1ubuntu3.6" OR banner:"Debian-2+deb12u3" OR banner:"FreeBSD-20240701")
We have a canned query named "Rapid Response: OpenSSH regreSSHion RCE - OpenSSH" that can be used to locate potentially impacted systems.
February 2023 (CVE-2023-25136) #
The OpenSSH team surfaced a security issue that specifically affected OpenSSH server version 9.1p1 (a.k.a. version 9.1). This version contained a memory double-free vulnerability (tracked as CVE-2023-25136) that could be reached pre-authentication by a remote attacker. Researchers, including JFrog and Qualys, had been investigating and providing proof-of-concepts of a denial-of-service scenario and remote code execution for the attacker.
What was the impact? #
OpenSSH is a popular open source implementation of the SSH protocol and is available on many operating systems. The installation base for OpenSSH is quite large (Shodan reported ~48k public-facing instances of OpenSSH servers running version 9.1).
The denial-of-service attack vector could be successful against a number of operating systems running OpenSSH 9.1. However, it yielded limited results because it only crashed the forked daemon instance that had been spun up to handle the attacker’s SSH connection (leaving the parent ssh daemon still running to handle other incoming connections).
Exploitation of this vulnerability for remote code execution (RCE) was more complex, with a current proof-of-concept that only targeted OpenBSD 7.2 without memory protections in place (such as ASLR, NX, or ROP defenses) and with code execution still contained within the ssh daemon’s sandbox. As researchers continued to investigate RCE exploitation, other operating systems with attacker-bypassable memory malloc and double-free protections might have been discovered. Thus, the ability to fully execute attacker-controlled code outside of the ssh daemon sandbox, even with memory protections in place, might have been achieved.
OpenSSH version 9.2p1 (a.k.a version 9.2) was released and patched this vulnerability (CVE-2023-25136). For systems currently running OpenSSH 9.1, admins were encouraged to update to OpenSSH 9.2 or later.
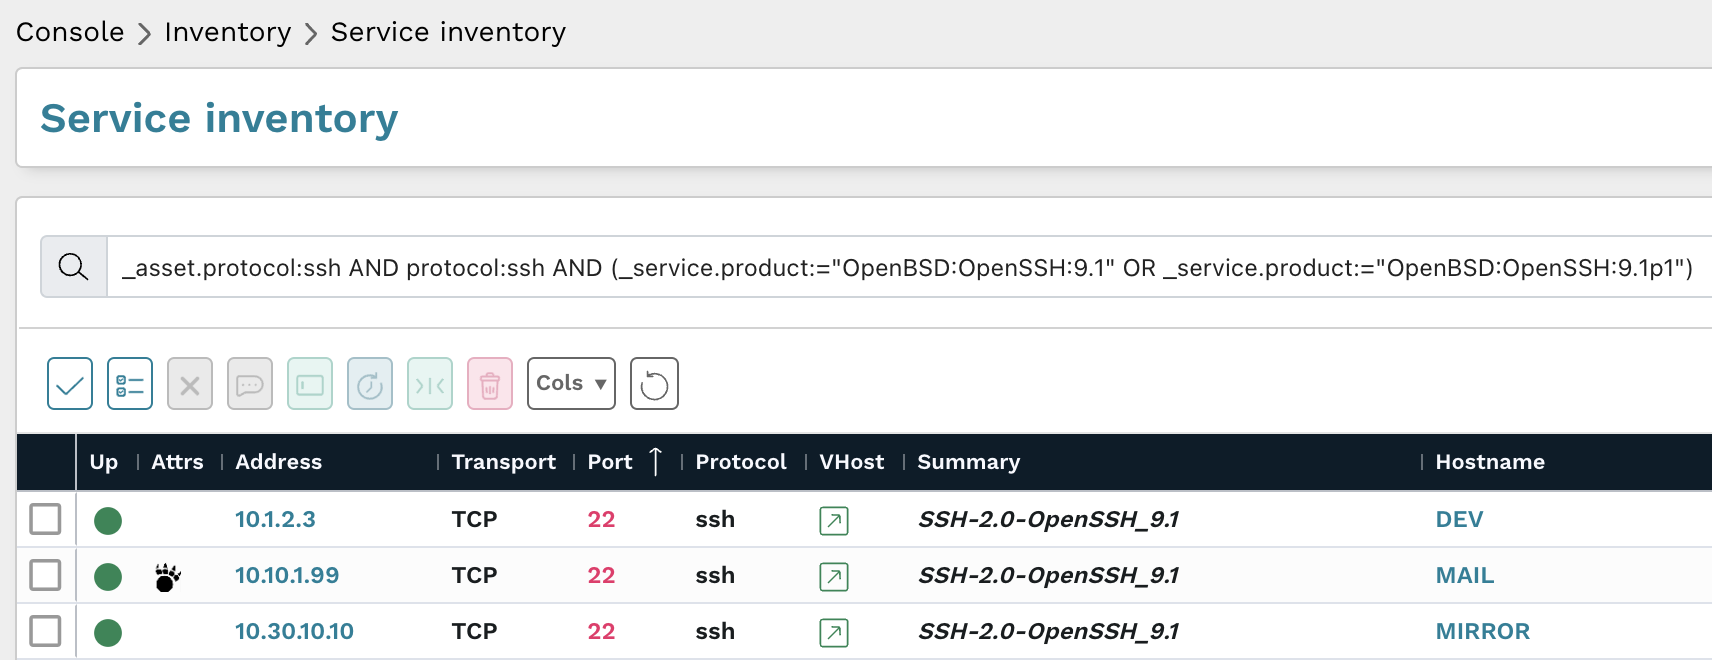
How runZero users found vulnerable 9.1/9.1p1 OpenSSH services with runZero #
runZero users located OpenSSH servers running the vulnerable 9.1/9.1p1 version on their networks using the following prebuilt query:
_asset.protocol:ssh AND protocol:ssh AND (_service.product:="OpenBSD:OpenSSH:9.1" OR _service.product:="OpenBSD:OpenSSH:9.1p1")
To locate all OpenSSH servers in your network, the following prebuilt query can be used:
product:”OpenSSH”
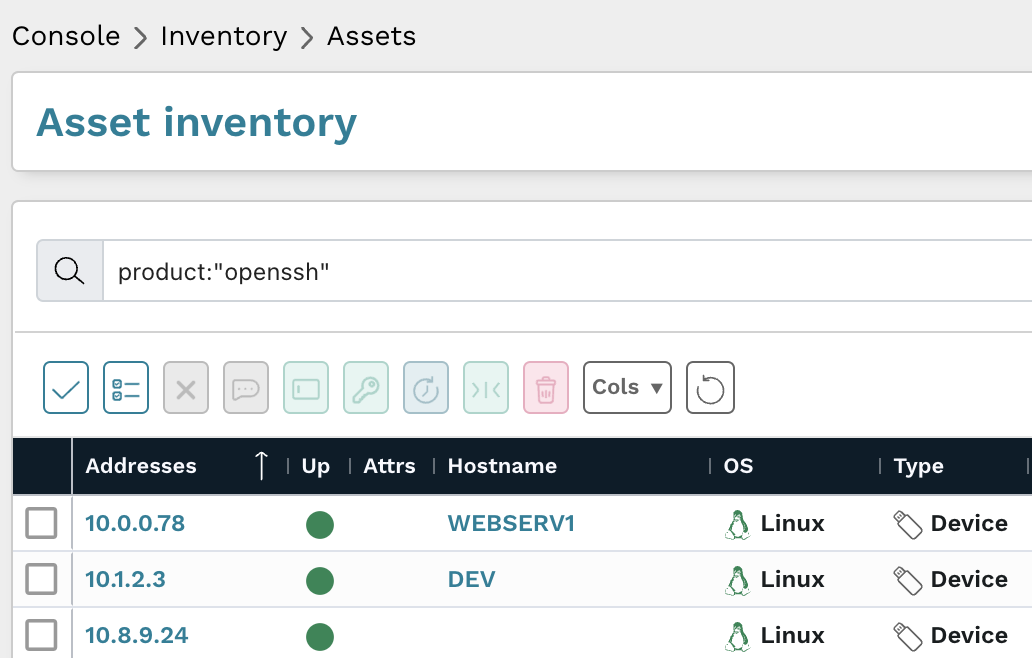
As always, any prebuilt queries are available from our Queries Library. Check out the library for other useful inventory queries.